Was CMMC Really Too Expensive? What the RFI Found
Mostly no. The DoW's own RFI puts CMMC itself near $47,000. The real cost is NIST 800-171, and it still applies.
Read more
Managed IT, cybersecurity and compliance services since 2010, backed by the operational depth of Cybertron International.
We run the IT for small and mid-sized businesses, and we handle the compliance work each one's industry requires: the controls, the documentation and the proof.
One team for the IT, the security and the compliance, so nothing falls between vendors.
Devices, servers, network, cloud, patching, backups and day-to-day support, run by a team against documented service levels.
Learn moreA real security layer in every engagement, built into the same stack that runs your operations.
Learn moreCMMC, NIST 800-171, HIPAA, FTC Safeguards and more, with the paperwork and the live systems owned by one team.
Learn morePCs, workstations and servers built on our own line, matched to the workload and the environment they run in.
Learn moreBackup and recovery judged by the only test that matters: how fast the server is running again.
Learn moreAI that runs where you control it, so sensitive and controlled data never leaves your hands.
Learn moreThe core service is Managed IT Services: your devices, servers, network, cloud, identity, patching, backups, vendor management, and day-to-day support, run against documented service levels by a team instead of a single point of failure. Every engagement carries a real cybersecurity layer, because in 2026 the two aren't separable.
Compliance is added to that where your industry requires it. Defense and federal suppliers get CMMC and NIST 800-171 readiness. Accounting and finance firms get the FTC Safeguards Rule program the regulation actually requires. Healthcare practices get HIPAA handled as an operating discipline instead of a dusty binder. The full picture lives on our Compliance Services page, and the principle is the same in every framework: the documentation and the live systems have to be owned by one team, or the paperwork drifts from reality and an audit finds the gap.
"I've worked with Cybertron for several years and they consistently go above and beyond to ensure that we have what we need promptly and accurately. [I] wouldn't want to work with any other company."
Stacey Bundy, Non Profit Medical Services
More client stories
Most calls come from owners weighing break-fix against an in-house hire against a managed partner, usually after one too many surprise invoices or a week of downtime that cost more than the IT bill. The rest come from regulated businesses: a supplier who just had CMMC flowed down by a prime, a CPA firm that read what the Safeguards Rule actually requires, a practice manager who knows the risk assessment is years stale. Both kinds of caller get the same first conversation, a straight read on where you stand and what we'd address first.
Plenty of firms can run your IT. The combination below is what you're buying: advice calibrated to what a business has to live with, not what looks most impressive on paper.
Managed IT, cybersecurity and compliance are our core work, and we have done them for businesses since 2010.
Added when your industry requires it and bundled into the same engagement, not sold as a separate project.
Documented service levels and a team behind them, so your business stops depending on one set of shoulders.
Through Cybertron International we have run production, inventory and a supply chain of our own, which keeps our advice practical.
From our headquarters in Wichita, Kansas, we work with businesses across the United States, in the industries listed here and most others. The rundown of what we see in each, and where the regulatory load sits, is on our industries page.
Plain answers on IT, security and compliance for business owners.
Mostly no. The DoW's own RFI puts CMMC itself near $47,000. The real cost is NIST 800-171, and it still applies.
Read more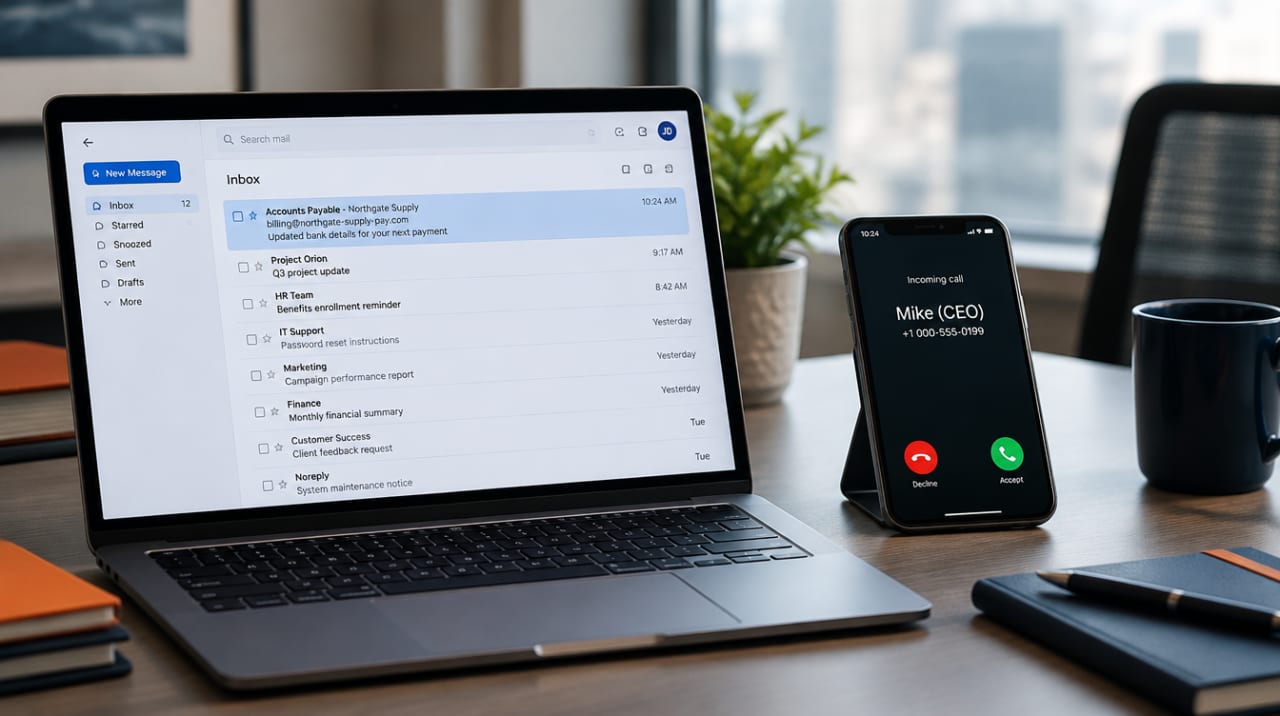
AI voice cloning, fake invoices, and "our bank details changed" emails are hitting small businesses. Here are the simple rules that stop them.
Read more
No federal CMMC grant exists yet. Here is what funding is real for defense suppliers, and the scoping decisions that cut the bill.
Read moreA free two-minute check on which workloads you should own instead of rent.
No. Most of our clients are ordinary businesses with no regulator in sight, and they get Managed IT Services with a serious security layer and nothing bolted on. Compliance work gets added when your industry requires it, and then it's bundled into the same engagement rather than sold as a separate project.
The ones our clients actually face: CMMC and NIST 800-171 for defense and federal suppliers, the FTC Safeguards Rule and IRS requirements for accounting and tax firms, HIPAA for medical and dental practices, GLBA for financial institutions, FERPA for education, PCI DSS where card payments flow. If yours isn't on that list, the approach is the same: we turn its requirements into action items, get them done, and keep the proof.
No. Co-Managed IT exists for exactly that situation. Your internal person keeps what they're good at, we bring depth where they're stretched, and the split is documented so it's clear who owns what.
No. We're a Registered Practitioner Organization, the role that prepares you and partners with you through readiness. The certification assessment is conducted by a separate accredited C3PAO. Two different roles, kept apart on purpose.
It depends on your headcount, your systems, and whether a compliance framework is in play, so we work the number out on the exploratory call against your actual situation rather than posting a figure that wouldn't fit it.
One step, not three. Book a 30-minute exploratory call and we'll give you a straight read on where you stand, what you're exposed on, and what we would actually look at first. No commitment, and if we're not the right fit, we'll say so on the call.
Book a call