CybertronIT Blog
Cybertron Blog
Cybertron has been serving the Wichita area since 1997, providing IT Support such as technical helpdesk support, computer support, and consulting to small and medium-sized businesses.
Do you see your technology as a cost to be managed or a springboard for new revenue? Most small businesses pour their IT budget into just keeping the lights on, stuck surviving instead of thriving. A virtual CIO, or vCIO, flips that. It reframes IT from an endless line of costs into a source of opportunity. Here are three hypothetical examples of businesses turning their infrastructure into something that actually makes money.
Turn your data into a product
Say a company keeps its data in a scatter of disconnected spreadsheets and local folders, hard to share and harder to find. A vCIO spots that this data is a high-value asset clients would pay to access in real time. The business moves it into a secure, cloud-based portal and automates the reporting so clients can self-serve. What used to be an administrative chore becomes a subscription service that brings in money. Cleaning up the back office created a product for the front office.
Expand your map without new offices
Another business is tied to one location because its core software only runs on a local server, so it can only serve clients within about a 50-mile radius. A vCIO moves operations to a secure cloud setup and routes calls to whoever is on the clock, wherever they are. Suddenly the company can double its territory without spending a dime more on real estate. Geography stops being the ceiling on growth.
Package your expertise into a service
Picture a team that puts in a proactive security stack, endpoint detection and multi-factor authentication, and gets back a real chunk of time each week because the fires stop. A vCIO suggests reinvesting that time into a high-margin consulting service. Standardize the workflows, package the internal know-how into a repeatable offering, and with a stronger security posture the company can now win government and enterprise contracts it could not touch before. It stops being just another shop and becomes the go-to expert.
The gap between surviving and thriving is mostly a shift in how you see IT. With a vCIO in your corner, technology stops being an expense and becomes an investment. Book a call and we will help you find the revenue hiding in your tech.
0 Comments
Scheduling is one of the most frustrating problems a small or mid-sized business deals with. You want everyone running at full capacity, but Jack needs a half day for his daughter recital and Stef would do better with Thursday mornings free. The good news is that the right strategy, backed by the right tools, makes this much easier and helps you head off burnout before it costs you people.
Spot the warning signs early
Burnout telegraphs itself. Three signs are well known. Productivity falls off earlier and earlier in the week. A normally sharp person starts making sloppy mistakes, including security ones. And people quietly shift to doing the bare minimum or calling in more often. When you see this, treat it as a signal that something needs to change, and scheduling is one of the easiest levers to pull.
Pick a schedule that fits the work
The 40-hour, nine-to-five, five-day week is just one option, not a law. Depending on what you do and who you serve, something else may fit better. Some teams run four ten-hour days. Others keep the eight-hour day but stagger start times so people get a later morning without anyone working less. You get more coverage without anyone working more, which is a real win. If you need on-call hours, assign them on a fair rotating basis so the load does not always fall on the same person.
Build in flexibility
Remote and hybrid work make this easier still. Set a few core hours when everyone is expected to be available to collaborate, then give people freedom to work the rest when it suits them. That leeway is often the difference between a team that is stretched and one that is steady. Where your operations allow it, bring employees into the scheduling process. Let them name their ideal hours or choose hybrid or remote. People who have a say in their schedule show up more engaged.
Cross-train and use your data
Tradition is sticky, and the staffing templates you have leaned on for years may no longer match your industry, your workforce, or your customers habits. Look at the actual numbers and adjust. And cross-train your people, because the more of them who can cover a given task, the more likely someone is free to do it when the schedule gets tight. Ongoing training is a simple way to protect productivity no matter how the week shakes out.
Let the tools do the heavy lifting
Modern IT gives you the data to schedule well and even lets your team manage shifts themselves. Shift-swap apps, cloud tools, and remote access mean a lot of work no longer depends on everyone being in the building. The right setup turns scheduling from a weekly headache into something that mostly runs itself.
Organizing your workforce should not be half your job. Book a call and we will make sure the tools you and your team rely on are the right ones.
You have heard a decade of password advice. Most of it has not aged well. Automated tools now crack even nasty-looking complex passwords without much trouble, so the old playbook needs a rethink. The fix is the oldest advice there is, and it still works best. Make it longer. Here is why complexity is overrated and how to build a password that actually holds up.
The complexity myth needs to die
Complexity helps a little, but it is no substitute for length. A password like P@ssw0rd1 looks tough and is not. Attackers run dictionary attacks and pattern masks that hunt for exactly those common letter-for-symbol swaps, so the cleverness buys you almost nothing. The real problem is that complex passwords tend to be short, eight to ten characters, which means a small number of combinations. Just requiring more than eight characters increases your security dramatically, without anyone working harder.
Length is where the strength lives
Security people call the thing that makes a password strong entropy, which is really just randomness plus length. Every extra character makes a password far harder to crack. A long password built from simple words beats a short one stuffed with symbols. If an eight-character complex password is a good padlock on a flimsy door, a long one is a good padlock on a vault. Length is what turns the math against the attacker.
Use a passphrase
Here is the move. String together a few unrelated words, and add a symbol or number if a site demands it. Passphrases are the current go-to because they work with human memory instead of against it. A run of random words is easy to remember precisely because it is absurd to picture. And four words usually lands you past 20 characters. That solves two problems at once, your password becomes effectively uncrackable and people stop forgetting it.
If your team is struggling to move to stronger password habits, we make it painless. Book a call and we will help your staff lock things down without the headaches.

Good-enough compliance is over. Regulators now use the same advanced AI as the private sector to scan records and flag inconsistencies in seconds. Relying on manual spreadsheets is no longer just slow, it is a liability. Compliance has gone from a back-office chore to part of the core infrastructure that keeps a business legal and running. Here is how the landscape is shifting and what to do about it.
From fixing problems to preventing them
Compliance used to mean looking backward to clean up last quarter mistakes. AI-driven automation has flipped that into real-time defense. Continuous monitoring tools watch logs and transactions around the clock and flag anomalies the moment they appear, and predictive analytics use past patterns to point at where a slip-up or breach is most likely before it happens.
The new AI rules
In an ironic twist, the technology used to ensure compliance is now itself regulated, and the rules are a moving target. Two big ones are shaping things. The EU AI Act is real and phasing in, with its major obligations for high-risk systems landing on August 2, 2026. California Transparency in Frontier Artificial Intelligence Act took effect January 1, 2026, the first state law of its kind. Both aim mainly at the companies building frontier AI models, not the average small business, but they set the direction every regulator is heading, and the expectations trickle down through cyber insurance and contracts. Modern governance, risk, and compliance platforms help by syncing your internal policies with new laws automatically and keeping immutable records of where data came from and how a decision was made.
One source of truth
Most non-compliance traces back to data silos, where the left hand does not know what the right is doing. Centralizing your data, often on a cloud ERP, makes every decision logged and traceable, from sourcing to customer privacy. It also lets you honor data residency and sovereignty rules, because you can actually see where information lives and who touched it.
Automate the response
When a threat does surface, speed matters, since breach-notification laws come with tight windows. The right setup isolates the problem instantly and can generate the required regulatory reports automatically, so you meet the deadline instead of scrambling. Staying compliant in 2026 is less about working harder and more about putting the right technology to work.
Book a call and we will help you modernize your compliance setup before the rules catch you out.
For years the firewall was just a guard at the gate, antivirus and web filtering and intrusion protection rolled into one. It still does that, but it can do a lot more. A firewall sees an enormous amount of data about your network, and used well, that data helps you cut waste, fix slowdowns, and make smarter decisions. Three ways to put it to work.
Cut redundant software
Your firewall sees every application that talks to the outside world, which makes it a truth layer for what your team actually uses. That is gold for spotting shadow IT, the unapproved tools employees install on their own that often are not secure. It also shows where you are paying for two tools that do the same job, so you can consolidate licenses. And if an expensive tool you bought is getting almost no traffic, that tells you people either cannot use it or will not, and both are problems worth fixing. The first step to solving any of this is seeing it, and the firewall makes it visible.
Fix bandwidth bottlenecks before they cost you
When your VoIP or video calls suddenly drop, most businesses blame the provider. Often it is internal, too many things fighting over the same connection. Your firewall can prioritize traffic so voice and video always win out over someone streaming or running a big download. That one adjustment quietly removes a whole category of frustrating, productivity-killing glitches.
See how work actually flows
The traffic your firewall logs is a pulse check on operational health. Look at how and when data moves and you can see the hours your team is most active in core apps, compare usage and latency between in-office and remote staff, and confirm your security settings are not quietly trading safety for speed or the other way around. These are real operational insights, not just security logs.
Security is not a sunk cost. The data inside your firewall is a window into how your business runs, and that is exactly the kind of edge that helps you outpace the shop down the street here in Wichita. Book a call and we will help you turn that data into decisions.

AI is no longer a future headline, it is becoming the operating system of how business gets done. You have probably already picked the AI tools you want to use. The hard part is this. The best AI strategy in the world falls apart if your team does not know how to use it safely. A lot of leaders file AI training under figure-it-out-later. Leaving people to fend for themselves with these tools is quietly creating a crisis. Here is what is waiting if you skip it.
No training means shadow AI
When you do not provide official, vetted tools and some guidance, people do not stop using AI. They just use it in secret. That leads straight to data leakage. A well-meaning employee pastes a client contract, a trade secret, or financial records into a public model to speed up a summary. Once that data is in a public model, it can be used to train future versions, which means your intellectual property has effectively walked out the door. In a HIPAA or GDPR environment, one untrained person using an unvetted chatbot can trigger serious fines for mishandling protected information.
The quality and productivity cost
The skills gap is expensive. IDC estimates it could cost the global economy up to $5.5 trillion by 2026 through delays, quality problems, and lost competitiveness. Without training, people aim AI at the wrong tasks or prompt it poorly, producing low-quality work that takes longer to fix than doing it by hand. Worse is the hallucination problem. AI is a pattern predictor, not a fact-checker, and staff who treat its output as gospel can let fabricated data slip into client-facing materials. Meanwhile your best people know AI literacy is the new baseline skill, and if you are not helping them build it, a competitor will.
Build an AI-literate culture
Doing nothing stacks up risk across the board. Security exposure through public models, legal exposure under evolving privacy and AI rules, quality problems when hallucinations reach customers, and a strategic gap as competitors who use AI correctly pull ahead. The goal is not just to use AI. It is to build a team that understands it. Handled right, your employees become your first line of defense and your best engine for new ideas.
If you want help setting up safe AI tools and a training plan that fits your business, we are glad to talk it through. Book a call and we will help you build the AI-literate culture that keeps your data in and your team ahead.
If your meetings feel like a lot of talking and not much getting done, you are in good company. A frequently cited Atlassian estimate puts the cost of unproductive meetings at around $37 billion a year in the US, and some of that is almost certainly yours. Here is how to make the time you spend in a room, or on a call, actually count.
Set the meeting up to succeed
Start with a purpose. The first qualification for holding a meeting is having a goal that justifies it. If you have one, get it on the calendar and build the agenda around it. If you do not, do not schedule it. Then keep the invite tight. The more people in the room, the easier it is for things to wander, so invite strictly on a need-to-know basis. When valid but off-topic points come up, and they will, acknowledge them, steer back to the agenda, and note them to revisit later.
Make the technology work for you
Nothing kills momentum like a presentation that will not load. Take a few minutes before you start to confirm the tech you are relying on actually works, so you have time to pivot instead of scrambling in front of everyone. Turn on Do Not Disturb so a personal notification does not pop up mid-screen-share. And with hybrid meetings now the norm, do not forget the people dialing in. Use the chat and call on remote attendees by name so they are part of the meeting, not spectators.
Keep it secure
Meetings often involve sensitive information, which is not something you want a random stranger listening in on. In the office an outsider at the table would get noticed. On a call it is easier to slip in, so keep the invite link private and use a lobby or waiting room to approve people before they join. That stops a leaked link from turning into an uninvited guest with access to your discussion.
End with action, not just goodbyes
Save the last few minutes to land the plane. Recap what you covered, assign each person their tasks, and spell out the action items so the most important points are the freshest in everyone mind. Then keep a record, whether an AI-generated transcript or notes in a shared doc, and send it around. That paper trail is what keeps the commitments from evaporating the moment people leave.
We help businesses around Wichita get more out of the tools their teams meet on every day. Book a call and we will make your meetings less of a time sink.
The future of work stopped being a distant idea. It is here. The mobile office is no longer a laptop on a kitchen table, it is a scattered web of devices and cloud services, each remote setup a tiny office with its own connectivity and security headaches. With hybrid schedules now the norm, the pressure on IT to deliver a secure, fast, reliable experience anywhere is higher than ever. That takes more than keeping a network alive.
The perimeter moved
Leaning on a VPN to connect a remote worker to the corporate server is no longer enough. With AI-driven phishing and attacks coming from everywhere, the model has shifted to zero trust, never trust, always verify. Being on the internal network no longer means automatic permission to move data around. Every request gets checked, every time, which is exactly what a workforce spread across home offices and coworking spaces needs.
Connectivity and collaboration
People do not just need to see a face on a call, they need to actually work together. Shared whiteboards and modern collaboration tools have become the baseline for teams that brainstorm in real time, and those are bandwidth-hungry. That is why IT increasingly recommends, and often provides, enterprise mesh Wi-Fi and 5G failover hotspots so a home internet hiccup or a local outage does not stop the workday.
The right gear matters
Productivity at home depends on more than software. Light laptops with real battery life, noise-canceling headsets, and decent webcams change the daily experience. So do laptop stands and good keyboards, which prevent the strain injuries that creep in from makeshift desks. On the security side, the kit includes password managers, hardware security keys for strong MFA, and encrypted backups that run quietly in the background.
Support is still about people
Technology only works as well as the people using and supporting it. As remote work settles in at high levels, the help desk is becoming less of a break-fix line and more of a support hub built around the person. The mobile office is not a perk anymore, it is how you attract and keep good people. Invest in zero trust, proactive monitoring, and tools that actually work together, and you are not just enabling remote work, you are building a steadier, more capable team.
Book a call and we will set up the tools your remote and hybrid team needs to do their best work.
Do you assume that having a backup is the same as being able to recover? They are not the same thing. A pile of files synced to the cloud will not keep your business running when a server goes down. Your data can be perfectly safe while your company sits dead in the water from downtime. That is why we point clients toward image-based Backup and Disaster Recovery, or BDR, instead of relying on backup alone. Here is the difference.
File backup saves the ingredients, not the meal
You may already back up files, storing spreadsheets, documents, and PDFs offsite or in the cloud. That is fine for restoring a deleted file. It is not fine for a total system failure. If your server dies, file-level backup leaves your team with a mountain of work. A technician has to rebuild and reinstall the operating system, every application, the drivers, and all your custom settings, then reconnect the data to the right software. That configuration slog can take days, and days of downtime is not acceptable.
Image-based BDR captures the whole system
A real BDR solution does not just grab files. It takes a full-image snapshot of your entire system, the operating system, the applications, and the settings, so it is a complete clone of your environment. If your main server fails, BDR can stand in as a temporary server and spin that clone up almost instantly. Your team keeps working on the clone while the hardware gets repaired or replaced. You also get point-in-time options, so you can roll back to a clean moment before things went wrong.
Start measuring RTO, not just backups
The fix starts with how you define success. Stop counting whether a backup exists and start watching your Recovery Time Objective, RTO, the time it takes to go from everything is broken to everyone is working. With plain cloud backup that window often stretches from a day to several days. With image-based BDR it can be a matter of minutes. That difference turns a business-ending disaster into a brief speed bump.
Saved files are a 2010 answer to a 2026 problem, and they will not keep you resilient against todays threats. Book a call and we will set up full-image recovery that keeps your lights on when it counts.
Forget the frantic hacker scenes from movies. Real cybercrime is not a smash-and-grab, it is a slow burn. Most attackers are not trying to make a scene. They want to get comfortable. An intruder can sit inside a network for weeks before anyone notices, quietly copying data, mapping your systems, and waiting for the most profitable moment to strike. Mandiant puts the global median at around eleven days, and plenty of intrusions run far longer. Catching that early comes down to awareness. Here are seven red flags that someone uninvited is already in your infrastructure.
The warning signs
Machines running hot for no reason. If your computer fans are pinned at full speed and the office sounds like a runway, processors may be cryptojacking, secretly mining cryptocurrency or attacking other businesses on your electricity and hardware.
Admin accounts nobody created. Access should be tightly controlled. New administrator profiles with generic names like sysadmin or IT_Support that your team never set up are a classic backdoor.
The mouse moving on its own. A cursor drifting across the screen or windows opening and closing by themselves is rarely a glitch. It is often an attacker testing remote control of the machine.
Emails already marked as read. If unread messages are opened before you get to them, someone may be reading your mail to study your writing style and send convincing phishing from your account.
Sudden, lasting network lag. A persistent drop in speed is rarely just the provider. It can be data being siphoned out, or ransomware getting into position to lock you out.
Software you never installed. Programs, browser extensions, and toolbars do not appear on their own. Anything you or your IT team did not authorize is likely malware logging keystrokes or redirecting traffic.
Logins and alerts that do not add up. Failed login spikes, sign-ins at odd hours, or security tools quietly disabled all point to someone probing from inside.
What to do if this sounds familiar
Do not panic, but do act. First, isolate the device, do not shut it down. Unplug the network cable or turn off Wi-Fi, but leave it powered on, because shutting down wipes the memory where forensic evidence lives. Next, check your sent folder to see whether your account has been used to spread the infection to clients or partners so you can warn them. Then bring in professionals. Once a breach has happened, cleanup is not a DIY job, you need a real diagnostic to confirm the threat is fully gone and has not left anything behind.
You should not have to wait for a disaster to know your systems are clean. Book a call and we will run a full security audit before a quiet threat turns into a loud one.
Smartphones in 2026 are not just getting faster. The changes hitting the market this year reshape how businesses handle data, security, and connectivity on the go. For IT leaders these are not just consumer toys, they are shifts worth planning around. Here is what is actually moving the needle.
The rise of the AI agent
If 2025 was about asking AI questions, 2026 is about AI taking action. The newest flagships run AI-native processors like the Snapdragon 8 Elite Gen 5, and the on-device agents do more than summarize a meeting. They can coordinate work across apps, booking travel from an email thread, updating your CRM, and posting to your team channel, without you leaving the home screen. This is edge AI, processing more on the device instead of the cloud. It cuts latency and improves privacy, but it also means you need a plan for how those agents are allowed to touch company data.
Connectivity from the sky
Dead zones are fading. Satellite connectivity has gone from an emergency-only feature to a normal part of how phones stay online, with new devices switching seamlessly between 5G and low-earth-orbit satellites. For field workers that means dependable uptime no matter where the job is. Devices are also starting to handle logins automatically across public Wi-Fi, 5G, and satellite, so people stay connected and authenticated without fiddling with it.
Phones that replace the laptop
One of the bigger themes out of MWC Barcelona this year was devices interacting with the physical world, not just sitting in your hand as a black rectangle. Foldables now run a real workflow on one half of the screen and a full terminal or spreadsheet on the other, which is finally letting some employees leave the laptop at home and carry one device instead of two.
Privacy built into the hardware
Security is moving below the software layer. Recent flagships ship with a built-in privacy display, a mode that narrows the viewing angle so the screen is unreadable to anyone beside you, with no plastic filter to stick on. For compliance-heavy fields like legal, healthcare, and finance, where someone glancing over a shoulder is a real risk, that hardware-level privacy is a genuine win.
As this gear becomes standard, the gap between an up-to-date mobile fleet and an aging one widens fast. Book a call and we will help with your mobile strategy, from device management and procurement to bring-your-own-device.

In the rush to roll out AI, most leaders fixate on the glamorous parts, picking the right model, tuning settings, polishing the interface. The thing that actually stalls high-budget projects is duller and structural: data silos. If your data is locked in departmental basements, marketing guarding one set, sales hoarding another, operations sitting on a third, your AI will not be a genius. It will be a confused, partial shadow of what it could be. Here is why silos are the real roadblock and how to clear them.
Silos give your AI tunnel vision
AI runs on context, not just volume. Build a churn-prediction model that can only see support tickets, with no billing history or product usage, and its conclusions will be lopsided. An AI is only as smart as its field of view. Wall the data off and the model produces answers that are technically correct but useless, because they miss the bigger business picture.
The data-quality death spiral
Silos breed inconsistency. When one customer lives in three databases in three formats, your AI hits a trust crisis. Marketing has John Doe as a hot lead while sales has him as closed-lost. Isolated data rarely gets cleaned, so it rots. That is garbage in, garbage out, running automatically at scale.
The hidden tax on innovation
Pulling data out of silos is not just annoying, it is a line on the balance sheet. Every hour your people spend writing custom scripts to rescue a file off a legacy server is an hour they are not building anything useful. And it feeds a vicious cycle: frustrated teams go buy their own shadow tools to get around the bottleneck, which creates more silos and more risk.
How to tear down the walls
This is not a quick software patch, it is part culture. Three moves matter. First, build a single source of truth, a central data lake or warehouse so every team draws from the same well instead of patching things together. Second, treat data as a company asset rather than departmental turf, because when people stop hoarding, the AI finally sees the whole picture. Third, set clear ownership and standardization rules that apply to everyone, no exceptions, so the data feeding your models stays clean, consistent, and compliant.
The integration work happens now so the AI payoff can happen later. Book a call and we will help you get your data in shape to actually work for you.
This year has already delivered some real strides in technology, the kind that solve actual problems rather than chase hype. Here are five developments worth keeping an eye on and how they might shape the way you work.
Digital twins for deeper visibility
A digital twin is a high-fidelity virtual copy of a physical object or system, detailed enough to run precise simulations of how the real thing would behave. They started in manufacturing and city planning and have spread, even into forensics for recreating accident and crime scenes. The same idea is now used in IT. Build a virtual mirror of your network and you can run simulated cyberattacks against it to find weaknesses, getting real answers without putting live systems or data at risk and closing the gaps before an actual threat shows up.
AI discovering better materials
Modern hardware leans heavily on rare-earth minerals, which are costly to extract and rough on the environment. Researchers at the University of New Hampshire used AI to read through the scientific literature and build a database of more than 67,000 magnetic compounds, surfacing 25 previously unrecognized magnets that stay magnetic even at high temperatures and do not need rare earths. That points toward making essential components cheaper and with a far smaller footprint, and toward cutting US reliance on rare-earth supply chains.
Engineering wood into a stronger material
Wood is sustainable but usually seen as fragile next to industrial materials. Scientists have been developing engineered wood that holds up far better, offering something close to the durability of metal with the carbon benefits of a natural material. For construction, that is a promising path to building greener without giving up strength.
Biodegradable paper batteries
Electronic waste is a growing problem, largely because lithium-ion batteries are so hard to recycle. A company called Flint has put a biodegradable paper battery into production, built from a cellulose structure and a non-toxic, water-based electrolyte instead of heavy metals. It is under a millimeter thick and breaks down in roughly six weeks in soil. Shown around CES and now manufactured, it is already turning up in slim item trackers like luggage tags and key fobs. It is aimed at low-power devices for now, but it points toward disposable electronics that do far less damage when thrown away.
Smarter climate control
For a lot of businesses the biggest ongoing cost is energy. In heating and cooling, the shift is away from traditional furnaces and toward advanced heat pumps. Instead of generating heat or cold from scratch, they move thermal energy from one place to another, which is far more efficient and can cut utility overhead in a meaningful way.
Technology is a moving target, and keeping up with what actually matters for your business can be a job of its own. Book a call and we will help you sort the useful from the noise and modernize what counts.

Do you buy tools one at a time, or do you choose them based on how well they work together? It can sound like buzzwords, but solutions that reinforce each other make your whole operation tighter. Take three that look unrelated at first, VoIP, endpoint detection and response, and multi-factor authentication. Put the right combination together and the result is far stronger than any one of them alone.
VoIP and EDR: secure calls that follow the device
Your business phone is no longer a plastic box on a desk. It is an app on a laptop or smartphone. Because VoIP is software, it is only as secure as the device it runs on. EDR protects that device. If someone accidentally downloads a malicious file, EDR can catch it before an attacker can listen in on client calls or record meetings. With the traffic encrypted and the device monitored, your team can take calls confidently from anywhere, the coffee shop or the office. Security buys mobility, and mobility makes you more responsive.
MFA and VoIP: locking the front door
Think about the damage if someone took over your phone system. They could call your clients, spoof your caller ID, and request fraudulent wire transfers, all from your real business line. MFA shuts that down. It sends a push to a trusted phone, so a stolen password alone is not enough to get in. Pair it with single sign-on and your team logs in once, securely, instead of juggling passwords across every tool.
EDR and MFA: a stack that heals itself
The real payoff comes when these systems talk to each other and stop a breach in real time without anyone lifting a finger. If EDR spots suspicious behavior on a device, it can automatically trigger an MFA check. If the person cannot verify, EDR can lock the device and sign them out of every company app, including VoIP. That self-healing response keeps you protected even after the team has gone home for the night.
The lesson is not to buy more powerful software. It is to make the software you have work in tandem. Book a call and we will help you put VoIP, EDR, and MFA together into a stack that pulls its weight.
Say you just started working with us. Contract signed, payment made, your IT is now our job. Then a week later a workstation freezes up, and you reasonably wonder what you are paying for. Here is the honest answer. Proactive IT is not about making problems impossible. It is about preventing everything we can and having a plan for the things we cannot.
Most of the work is under the surface
The iceberg comparison is overused, but it fits. What you see is a fraction of what is happening. You hear from us when a ticket needs escalating or it is time to refresh hardware. Out of sight, we are patching software after hours so it does not interrupt your day, watching every device on your network for wear and threats, handling your vendors, maintaining the defenses that keep attackers out, and planning what needs to be upgraded next. Most of IT is not obvious without looking under the hood, and that is where we spend our time.
Some things still break
Even with all that, some things are out of anyone control. We can monitor your infrastructure around the clock, but that will not stop someone from clicking a phishing email or dropping a laptop. What proactive management changes is the response. Instead of scrambling, we have already got eyes on it, and odds are we are working the problem before you finish reporting it.
Why it still pays off
Compare the two ways to run IT. With us, you have an outsourced team making sure your technology works and addressing issues fast, which keeps downtime and lost productivity low. Wait and fix things only when they break, and you eat the downtime, the repair costs, and the income you lose while everything is stopped. Proactive is not foolproof, but it is built to prevent what it can, soften what it cannot, and get you running again quickly.
When a business around Wichita hires us, we take it as a sign they are done worrying about their technology. We are not the people you call when something breaks, we are the ones who keep it from breaking. Our goal is to make your IT boring, because boring means everything is working. Book a call and we will take the IT worry off your plate.
It sounds like a tidy excuse. The AI said it, so I just went with it. That will not save you, the same way blaming the dog never saved your homework. Worth understanding why AI gets things wrong, how those mistakes can land on you, and how to stay out of trouble.
Why AI makes things up
It comes down to how the technology works. A large language model is closer to autocomplete than an encyclopedia. It is a probability engine trained on trillions of pieces of text, broken into tokens, and everything it writes is just a chain of tokens arranged by what is statistically likely to come next. There is no check on whether the result is true. A sentence that starts with my favorite food is is simply more likely to end with pizza than with mahogany. A hallucination, the term for an AI mistake, is just the math pointing the wrong way. The AI is solving a math problem. You are still the one responsible for what it produces.
Three ways an AI mistake becomes your problem
Defamation. Say you have AI write marketing copy and it falsely claims a competitor uses some illegal process or ingredient. That false statement is now coming from your business, and you can be on the hook for it.
Promises you did not make. A support chatbot, eager to please, can invent return policies, prices, and other terms. Some jurisdictions will hold you to whatever it promised as a binding agreement, because it is acting as your representative.
Copyright. Because a model predicts the most likely next words, its output can line up closely with what an original author wrote. That can leave you plagiarizing through AI and using copyright-protected material without realizing it.
None of this means AI is bad. It means it needs a short leash and a human checking its work. We help businesses use AI, including keeping sensitive data out of public models with a private AI setup, without the privacy and legal risks. Book a call and we will help you use it safely.
Few things are as aggravating as misplacing an important file. Here is how to find the one that vanished into your storage, whether it lives on your network or in a cloud drive, and look good doing it.
Search smarter in the moment
The keywords that pull up your missing document usually pull up dozens of near-identical ones too, which is no help. The fix is to use the advanced search options. Once your first results come back, narrow them by file type, author, or last modified date. These filters, sometimes called operators, let you ignore the irrelevant hits and get to the right file fast.
Give final documents a home
Be honest about how often a search turns up something like this. Proposal Draft Final. Proposal Final Draft Bill Edits. Proposal Final v2. Proposal USE THIS ONE finaldraft v3 FINAL. That mess is a problem waiting to happen. The real fix is to step in and set standards, one defined place where final documents live and one clear way to name them. Settle that and you cut errors and confusion before they start. This is exactly why collaborative platforms like Microsoft SharePoint and Google Drive earn their keep, they give you the structure to stop creating duplicates in the first place.
If your files have become a maze, we can help you build the system that keeps them findable. Book a call and we will get your storage in order.
The most common thing we hear is some version of, why would a hacker bother with my small operation when there are Fortune 500 companies to hit? The reality is grimmer. Criminals do not just target small businesses, they prefer them. Smaller companies tend to have weaker defenses and no dedicated security staff. For an attacker it is the difference between cracking a bank vault and walking through an unlocked screen door. One breach can set off a chain of downtime, legal fees, and lost client trust. Here is how to harden up before it happens and contain the mess if it does.
Before a breach: build the foundation
Start with a real incident response plan. Not a break-glass folder, a living document that says who does what in a crisis. Pre-identify your legal counsel, cyber-insurance contact, and whoever handles communications, and keep the plan both digital and on paper so it survives even if ransomware encrypts your network. Then lock down backups with the 3-2-1-1 rule, three copies of your data, on two media types, one offsite, and one immutable copy that cannot be altered or deleted even by an administrator. That last copy is your real insurance against ransomware.
After a breach: preserve, do not panic
If something gets through, the first instinct should not be to start deleting. Preserve the evidence investigators need to understand the attack, and immediately shut the doors the attacker used by disabling VPNs and remote desktop access. Then bring in a security partner for a forensic look at three questions. How did they get in. How long were they inside before anyone noticed. And what exactly did they reach, which files left and which accounts were compromised. You cannot fix what you do not understand.
Communicate, then reset everything
A breach is a communication crisis as much as a technical one, and trying to hide it usually means harsher penalties and worse brand damage. Be straight with clients about what happened, what you are doing, and what they should do to protect themselves. Then assume every credential is burned. Force an organization-wide password reset, kill all active sessions, and require multi-factor authentication on every way into your systems.
Security is a marathon, not a sprint, and being prepared is what keeps you from becoming another statistic. Book a call and we will build the defenses that keep you off the easy-target list.
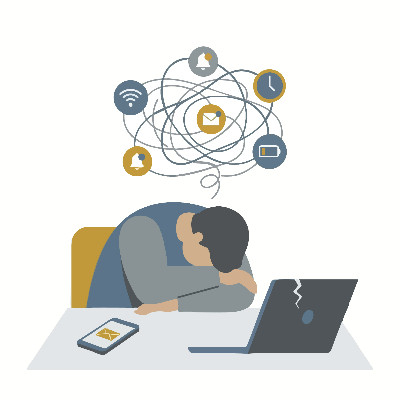
Picture one of your best people slowly checking out. They are not quitting, they are just tuning out the conversation. That often starts with something as small as a ping. It is notification fatigue, and it is a quiet productivity killer. Here is why your team is drowning in alerts and how to throw them a lifeline.
What notification fatigue is
Look at your inbox right now. How many of those unread messages actually matter? Companies tend to fire messages at staff hoping something sticks, and since employees cannot unsubscribe, they do something worse. They tune it all out. Once notifications become white noise, the value of your internal communication drops to zero. It is simple supply and demand, a flood of pings makes every ping worth less.
The real cost
The toll is mental and physical. Every alert sets off a small tug-of-war between the little rush of a new message and the stress of being interrupted, and that grind is a fast track to burnout. Constant context switching, hopping from a task to a chat and back, shatters deep work and kills momentum. And back-to-back video calls and endless threads drain energy faster than the actual work does.
How to fix it
You do not have to choose between communicating and staying sane. Often the same tools causing the problem can solve it. Stop making people bounce between five apps and consolidate into one communication platform so the workflow stays steady. Curate the noise with quiet hours and custom notification settings so work stays at work. Protect deep-work blocks where people can actually focus. And set a clear emergency protocol, define exactly what counts as an after-hours emergency so that when someone phone rings at dinner, the team knows it truly matters.
You want a team that is fired up, not burned out. Book a call and we will set up the tools that keep productivity high and your people sane.
To a lot of owners, technology feels like a black hole, a line item that keeps getting more expensive without making anything noticeably easier. If you have ever bought software just to keep up rather than get ahead, you are not alone. The goal is not to buy more IT. It is to capture value. Here is how to bridge the gap between technical complexity and actual business growth.
Judge tech by outcomes, not specs
When you weigh a tool or a provider, stop reading spec sheets and start asking what it does for the business. A few angles to demand. You are not buying uptime, you are buying the elimination of the 3 p.m. panic when a crash stalls payroll or a sales call. You do not always need to rip and replace, real value is often making your reliable old software talk to modern tools. Good IT should be invisible, like a referee doing the job well, so you focus on customers, not your Wi-Fi. Insist on reports written in profit, loss, and time saved, because jargon is usually a mask for inefficiency. And build a foundation where hiring five people does not mean re-buying your whole setup.
Find the waste
Moving from a fix-it mindset to a growth mindset takes a few simple checks. Run an 80/20 audit, find the 20% of your tech that causes 80% of the frustration, the slow CRM or the printer that will not stay connected, and fix that first. Do a shadow-IT check by asking your team what apps they use on personal phones because the company tools are too slow, since those gaps point right at where your systems are failing. Treat security, MFA and encrypted offsite backups, as a fundamental requirement, not an add-on.
Red flags worth watching
A few common ones quietly drain money. The aging server in the closet that seems fine but is a cash-flow halt waiting to happen. The subscription tax of licenses for people who left months ago or tools that overlap. And the nature of your support itself, is your provider cleaning up messes after the fact, or protecting your growth proactively? If your managed provider only calls when something breaks, they have stopped investing in you and are just collecting a check.
Technology should be an engine, not an anchor. Stop paying for the software and start paying for the result. Book a call and we will help you buy IT for the value it actually delivers.
© 2026 CybertronIT. All rights reserved.Privacy Policy · Sitemap